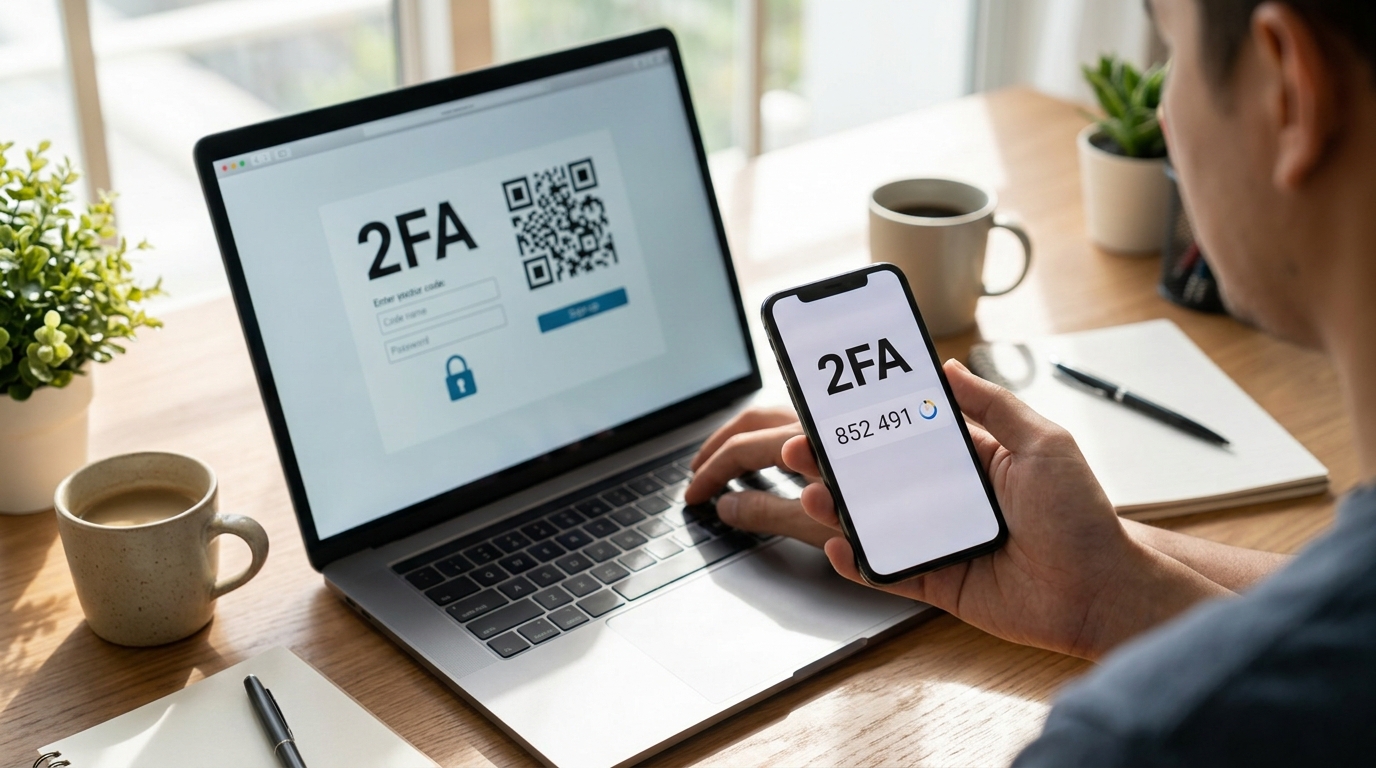
¡Protege tu información personal y mantén a raya a los hackers con la autenticación de dos factores! ¿Alguna vez te preguntaste cómo puedes hacer que tu cuenta sea más segura? La autenticación de dos factores es la respuesta a tus preocupaciones de seguridad en línea. Aprende cómo configurar esta capa adicional de protección en tus cuentas en solo unos simples pasos. ¡No te arriesgues a ser víctima de un ataque cibernético, sigue leyendo para saber más!
What is Two-Factor Authentication?
Two-Factor Authentication (2FA) is a security process that requires users to provide two different authentication factors to verify their identity before gaining access to an account or system. The first factor is typically something the user knows, like a password, while the second factor is something the user possesses, such as a smartphone or a hardware token. By requiring both factors, 2FA adds an extra layer of security and makes it harder for unauthorized users to access sensitive information.
Benefits of Two-Factor Authentication
Implementing Two-Factor Authentication (2FA) offers several key benefits for both individuals and organizations. Firstly, it significantly enhances security by reducing the risk of unauthorized access, data breaches, and identity theft. Secondly, 2FA provides an additional safeguard against phishing attacks and other forms of online fraud. Furthermore, using 2FA can help organizations comply with industry regulations and demonstrate a commitment to protecting user data and privacy. Overall, the adoption of 2FA is a proactive measure to bolster cybersecurity defenses and safeguard sensitive information.
Benefits of Two-Factor Authentication
Two-Factor Authentication (2FA) offers a crucial layer of security for online accounts by requiring users to provide two forms of identification before gaining access. This additional step beyond the traditional password significantly enhances security measures. One of the primary benefits of 2FA is the mitigation of unauthorized access, as even if a hacker manages to obtain a user’s password, they would still need the second factor to breach the account. This extra security measure helps protect sensitive data, personal information, and financial assets from potential cyber threats.
Enhanced Security
By implementing Two-Factor Authentication, organizations and individuals can significantly reduce the risk of unauthorized access and data breaches. Even if a password is compromised, the additional authentication factor acts as a robust defense mechanism against cyber threats. This heightened security not only safeguards sensitive information but also enhances user trust and confidence in the protection of their accounts. Embracing 2FA as a security best practice can contribute to a more secure online environment for both businesses and individuals.
Benefits of Two-Factor Authentication
Implementing Two-Factor Authentication (2FA) provides an additional layer of security beyond just a password. By requiring users to provide a second piece of information to verify their identity, such as a code sent to their phone or a fingerprint scan, 2FA significantly reduces the risk of unauthorized access to sensitive data. This extra step helps to thwart various cyber threats, including phishing attacks, password breaches, and brute-force attacks, enhancing overall security posture.
How to Enable Two-Factor Authentication
Enabling Two-Factor Authentication (2FA) is straightforward and varies depending on the platform or service you are using. Typically, you can navigate to your account settings, locate the security or privacy section, and find the option to enable 2FA. Once activated, you may need to link your account to a mobile device or authenticator app to receive verification codes. It’s essential to follow the setup instructions carefully to ensure a seamless and secure activation of 2FA for your accounts.
Types of Two-Factor Authentication Methods
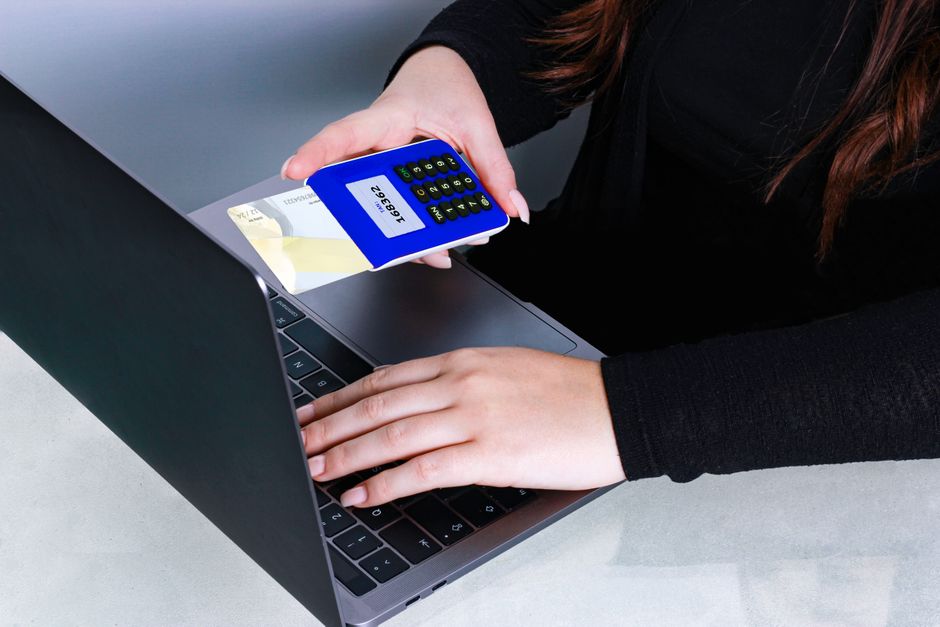
Two-factor authentication (2FA) methods offer different ways to enhance security by requiring users to provide two different factors to access an account. The most common methods include SMS codes, authenticator apps, biometrics, hardware tokens, and email verification. SMS codes involve receiving a one-time code via text message, while authenticator apps like Google Authenticator generate codes on smartphones. Biometrics, such as fingerprint or facial recognition, provide a unique physical characteristic for verification. Hardware tokens are physical devices that generate codes, adding an extra layer of security. Email verification sends a code to the user’s email address for login confirmation.
Each method has its strengths and weaknesses, with some being more secure and convenient than others. It’s essential to consider factors like user accessibility, cost, and ease of implementation when choosing the most suitable 2FA method for your organization. Implementing multiple 2FA methods can provide added security layers to protect sensitive data and prevent unauthorized access.
Types of Two-Factor Authentication Methods
Two-Factor Authentication (2FA) offers various methods to add an extra layer of security to your accounts. One common method is One-Time Passwords (OTP), which generates a unique code that users must enter along with their password. Another method is Biometric Authentication, using fingerprints, facial recognition, or voice patterns to verify identity. Additionally, Hardware Tokens provide physical devices that generate codes for authentication. SMS-based codes and authentication apps like Google Authenticator are also popular choices. Each method has its strengths and weaknesses, so choosing the right one depends on factors like ease of use, security level required, and user preferences.
Best Practices for Two-Factor Authentication
Implementing Best Practices for Two-Factor Authentication is crucial to maximize security. Firstly, Enable 2FA Everywhere Possible to protect all your online accounts, not just the most sensitive ones. It’s also recommended to Use Different Authentication Methods for different accounts to enhance security further. Regularly updating your authentication methods and Regularly Reviewing Account Activity to detect any suspicious behavior are essential practices. Lastly, educating users on the importance of 2FA and providing clear instructions on how to enable and use it can significantly improve overall security posture.
Troubleshooting Two-Factor Authentication
If you encounter issues with your Two-Factor Authentication setup, don’t panic. Troubleshooting common problems can help you regain access to your accounts securely. One common problem is incorrect entry of the verification code. Double-check the code you entered to ensure accuracy. If you’re still having trouble, try refreshing the authentication page or generating a new code. Additionally, ensure that your device’s time and date settings are accurate, as discrepancies can cause authentication failures.
Another frequent issue is compatibility problems with the authentication app or device. Make sure you are using a supported app and that your device meets the system requirements. If problems persist, consider reaching out to the service provider’s support team for further assistance. By following these troubleshooting steps, you can address common Two-Factor Authentication issues effectively and enhance the security of your accounts.